ThreatOrigin

Your data stays in your hands, and yours alone

Analyze all DNS traffic on your own servers. Logs, user details and reports stay inside your network, and threat hunting runs there too.

Threat hunting that keeps personal data in-house

Most solutions face a hard trade-off: they skip user traffic to avoid compliance risks, leaving you with critical blind spots. Because they can't separate the threat from the identity, they often have to exclude both.

ThreatOrigin bridges this gap. Our on-prem Privacy Module processes the full traffic data on your own servers, so you get visibility into every signal while user details never have to leave your environment.
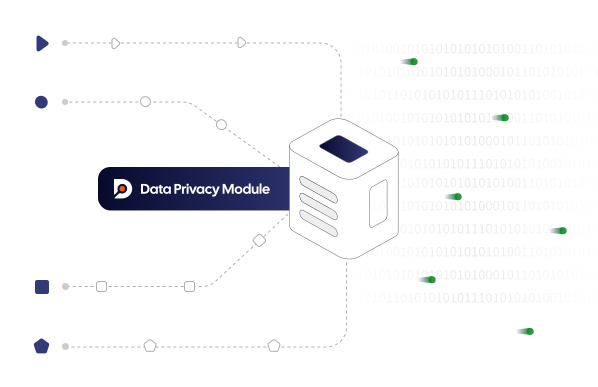
ThreatOrigin Data Privacy Module processing traffic with encryption

Stay compliant without going blind

Threat hunting, correlation and reporting all run inside your own environment, and the data stays under your control. Your security team keeps the visibility it needs to detect and investigate threats.
ThreatOrigin Privacy Module processor chip visualization

Turn every alert into a fully resolved story

Connect every DNS event to the real device and context behind it, across any network topology. Let investigations move from a single signal to the precise endpoint—without exposing personal data.
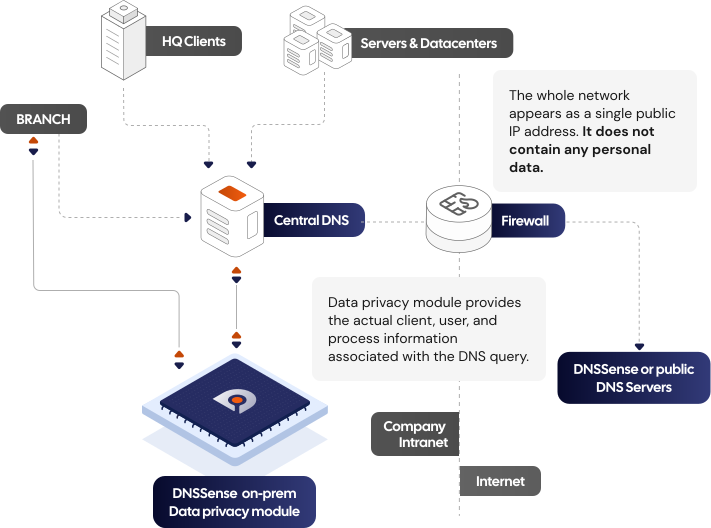
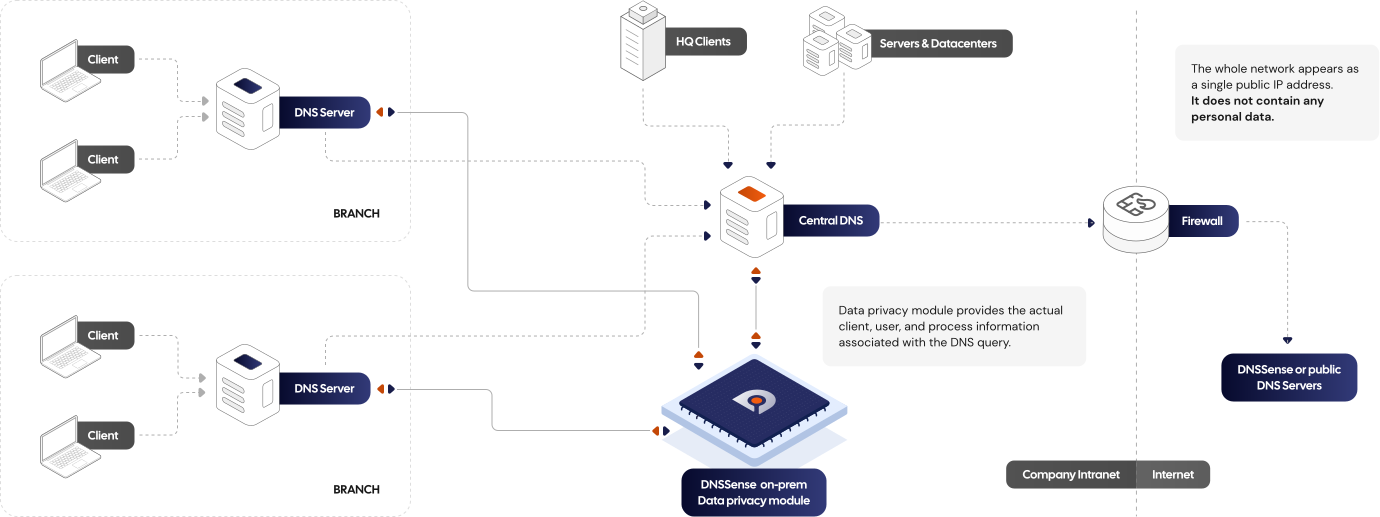
Network topology diagram showing how ThreatOrigin connects DNS events to devices through the on-prem Data Privacy Module
DATA PRIVACY → KEY FEATURES

Engineered to solve the privacy-security paradox

Visibility and privacy usually pull in opposite directions. Keeping the analysis inside your network lets you have both.
Rich context feature illustration

Rich context, kept in-house.

Automatically link every DNS signal to its user, device, and process context by ingesting local AD and XDR data in real-time. This shows your team who did what, while the logs and the correlation stay on your own servers. By processing this correlation on-prem, you eliminate the friction between security needs and privacy laws, so threat hunting can go deep without moving personal data out.
Integration feature illustration

Fits your network as it is.

The Privacy Module sits passively next to your existing DNS servers and Active Directory and reads their logs; nothing in your network changes. It also works with your SIEM and XDR.
Access control feature illustration

Your users, your groups.

Write rules and read reports by the users and groups you already manage in Active Directory and Microsoft Entra ID. Assign a policy to a group and its members update automatically, so access follows your own directory.

There's more to discover !

Sensei

Hey, I'm Sensei

I can walk you through everything about ThreatOrigin's data privacy feature. What's on your mind?